API Security Audit: Lock Down Endpoints & Prevent Data Breaches
Verify authentication integrity, enforce granular access controls, and shield business endpoints against scraping, abuse, and data theft.
Where Bottlenecks Impact Your Customers & Revenue
Real-world friction, checkout hesitation, and performance barriers that directly reduce conversions and customer retention.
Unauthorized Data Scraping & Competitor Exposure
Unprotected public API endpoints allowing competitors or malicious actors to bulk-harvest your pricing, customer, or catalog data.
Broken Object-Level Authorization (BOLA/IDOR)
Missing ownership verification allowing authenticated users to manipulate URL IDs and access other customers' private accounts.
Denial of Service from Unrestricted Resource Demands
Endpoints lacking strict rate limiting and request timeouts can be taken down by simple automated scripts, halting business operations.
Compromised Authentication & Token Hijacking
Improper JWT validation and insecure session management allowing attackers to impersonate administrative users.
How We Fix It: The 14-Day Performance Sprint
A structured, milestone-driven engineering roadmap delivered directly into your staging repository with zero downtime.
Endpoint Discovery & Fuzzing
OpenAPI/GraphQL schema discovery, endpoint mapping, and automated fuzz testing.
Object-Level Authorization Audit
Validation across all state-mutating endpoints (POST, PUT, DELETE) and tenant boundaries.
Distributed Rate-Limiting Layer
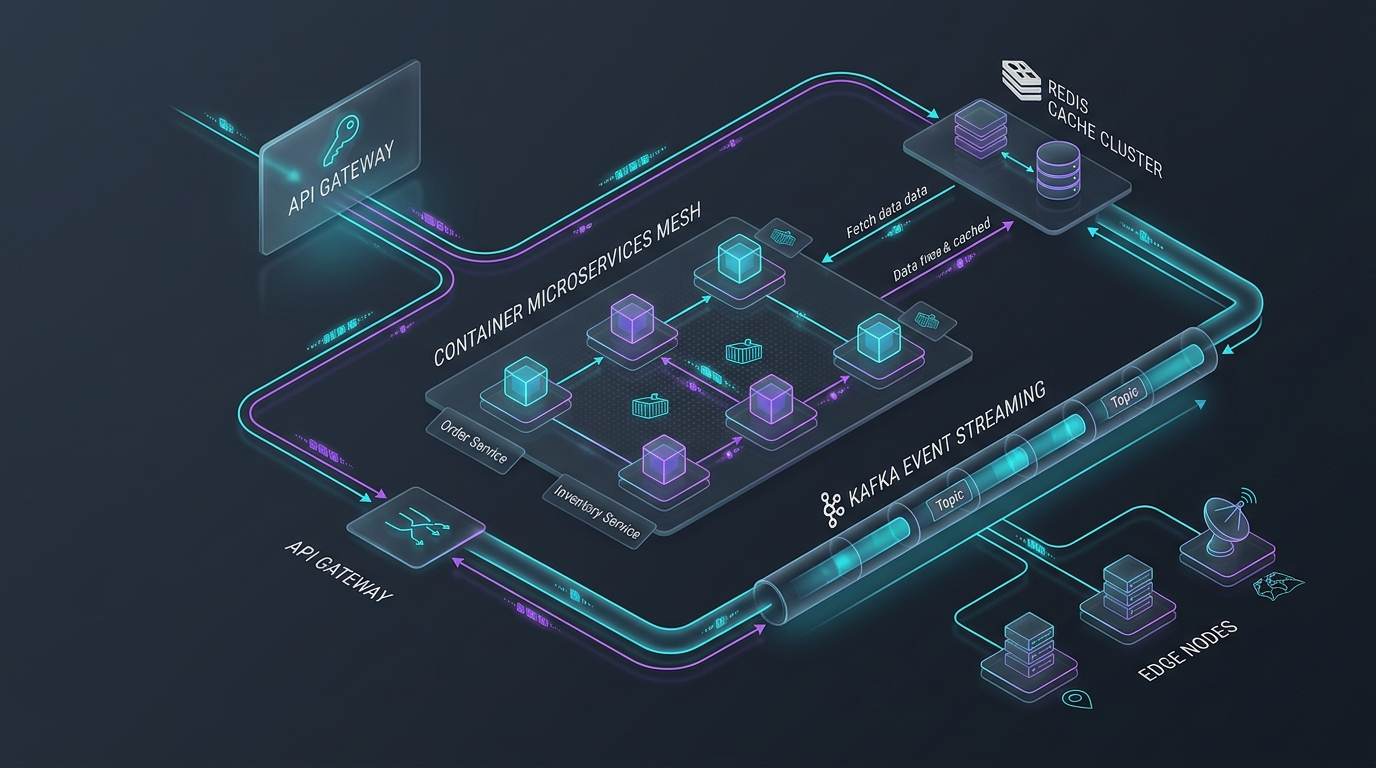
Architecture and implementation of Redis-backed distributed rate limiting at the gateway layer.
Token Verification Hardening
Hardening JWT signing, implementing short-lived access tokens with secure HTTP-only refresh tokens.
Penetration Re-Test & Handover
Final penetration re-test, OWASP API Top 10 compliance validation, and team security handover.
Tangible Business Outcomes in Your Codebase
What your executive and engineering leadership receives in your production repository. Zero theoretical slide decks—only verified speed improvements, clean code diffs, and documented operational stability.
API Vulnerability Assessment Matrix
Complete endpoint inventory mapping authorization strength and vulnerability remediations.
Rate Limiting & Auth Middleware
Tested middleware implementing Redis token-bucket rate limiting and cryptographically sound JWT parsing.
Automated API Security Test Suite
Integration test suite running inside CI/CD to prevent BOLA regressions.
PropTech SaaS Platform ($12M ARR)
4 BOLA vulnerabilities exposed tenant lease agreements; API abused by external scrapers consuming 40% of database CPU.
Explore Audit Scope ↗Verified Production Telemetry Delta
Authorization middleware deployed across 140+ endpoints; Redis rate-limiting eliminated scraper abuse; 0 unauthorized accesses.
Related Engineering Workstreams
Need source-level application security audits? Explore our Security Code Review services.
Looking to optimize API response times? Check out our API Performance Optimization services.
Lock Down Your API Layer
No exploratory sales calls. Direct asynchronous code remediation and engineering triage.
Full non-disclosure agreement guaranteed prior to review.